HelloID Sign-In
Overview
Districts that use HelloID (Tools4Ever) can let their people sign in to Manage1to1 with it. A Sign in with HelloID button appears on the Manage1to1 login page, and HelloID signs the person in based on who they are: administrators land in the admin area, and all other users land in their Manage1to1 portal.
HelloID uses SAML 2.0, so this is a per-district setup: you connect HelloID by pasting its metadata, hand a few values to your HelloID team, and enable it. A HelloID account whose email does not match an existing Manage1to1 admin or user is not granted access (single sign-on never creates new accounts).
To configure SSO, you need the Manage Settings permission assigned to your role.
What you'll need from HelloID
Work with your HelloID administrator to add a SAML application for Manage1to1 in HelloID Access Management, then collect:
- The HelloID SAML metadata (a metadata URL is easiest; metadata XML also works).
You will also hand a few Manage1to1 values back to your HelloID team, shown on the SSO Settings card once you open it (next section).
Step 1: Open the HelloID card
- Go to Settings → SSO Settings.
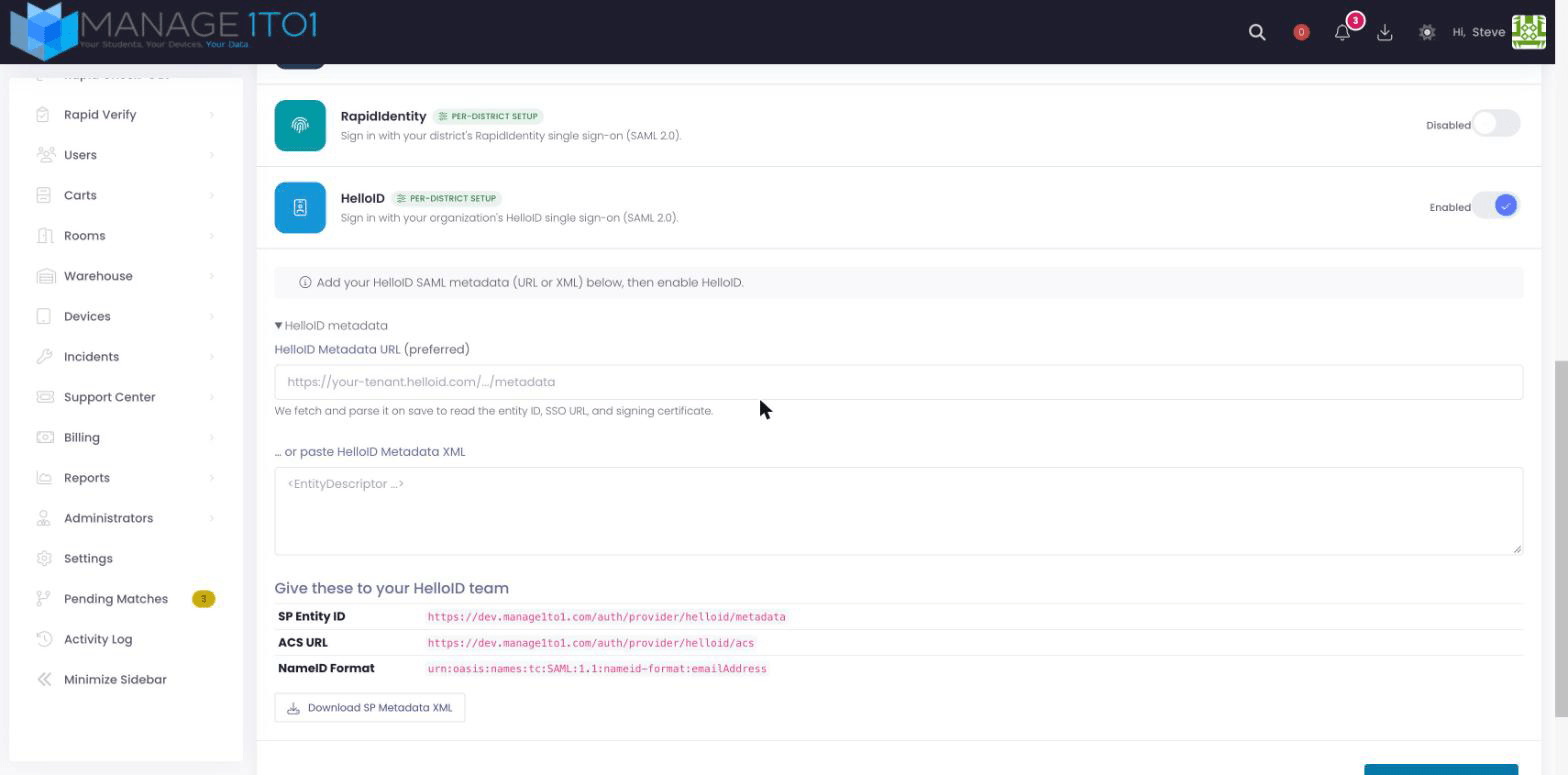
- Find the HelloID row and turn on its toggle to reveal the configuration panel.
The panel shows a metadata box and, under Give these to your HelloID team, the Manage1to1 service-provider values (SP Entity ID, ACS URL, and NameID Format) plus a Download SP Metadata XML link.
Step 2: Connect HelloID
- Paste your HelloID Metadata URL (preferred) or Metadata XML into the panel. Manage1to1 reads the entity ID, SSO URL, and signing certificate from it.
- Give your HelloID team the SP Entity ID, ACS URL, and NameID Format shown on the card (or the downloadable SP metadata), so HelloID knows where to send people and releases an email address in the assertion.
- Click Save SSO Settings.
Once saved, the card shows Connected with a Test sign-in link you can use to confirm the round trip end to end before rolling it out.
Manage1to1 matches each person by email, so HelloID must send an email address in the assertion (as the NameID in emailAddress format, or in a standard email attribute). If sign-in reports no email, ask your HelloID team to add the email claim.
How sign-in routes users
When someone signs in with HelloID, Manage1to1 matches their email to an account and routes them:
- Administrators land in the Manage1to1 admin area.
- All other users (staff, students, guardians) land in their Manage1to1 portal.
- No matching account is bounced back with an "invalid credentials" message. Single sign-on does not create accounts.
A HelloID sign-in is recorded in the user's profile login history as a HelloID SSO sign-in, the same as any other sign-in method.
Troubleshooting
- "Invalid credentials" after signing in with HelloID. The person's HelloID email doesn't match an existing Manage1to1 admin or user, or no email was released in the assertion. Add or correct the account in Manage1to1, and confirm HelloID sends an email address, then try again.
- The button doesn't appear on the login page. HelloID is enabled only once a connection is saved. Open the HelloID card, paste your metadata, and save.
- The connection won't save. Manage1to1 could not read an entity ID, SSO URL, or signing certificate from the metadata. Re-copy the metadata URL or XML from HelloID and try again.